Our approach
A disciplined way to run what matters
Clear phases, measurable service levels and security designed into every layer. Here is exactly how we work with you.
How we work
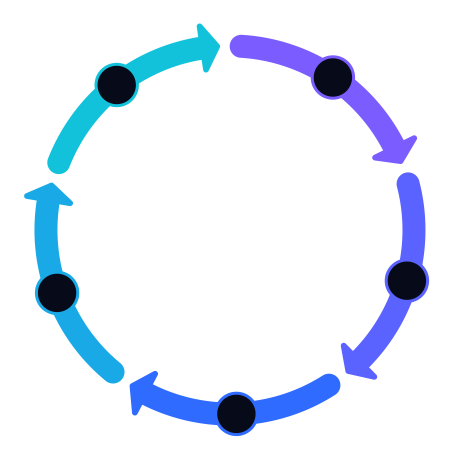
One continuous loop, from build to recovery
Every engagement follows the same operating loop. Each turn makes your platform faster, cheaper and harder to break.
- 01
Build
Landing zones, pipelines and infrastructure as code, reviewed and repeatable.
- 02
Run
24/7 operations, patching, scaling and cost control by one accountable team.
- 03
Observe
Full-stack monitoring, alerting and service-level tracking you can see live.
- 04
Recover
Replication, failover and recovery runbooks that are tested, not assumed.
- 05
Improve
Post-incident reviews, FinOps and tuning fed straight back into the next build.
Engagement model
From first assessment to steady-state operations
A clear, phased path with defined outputs at every step, so you always know what happens next.
-
Phase 01
Assess
2–3 weeks- Architecture and risk review
- Cost and resilience baseline
-
Phase 02
Design
3–4 weeks- Target architecture
- RPO and RTO per workload
-
Phase 03
Build & migrate
6–12 weeks- Landing zone as code
- Migration in planned waves
-
Phase 04
Operate
Ongoing- 24/7 operations and support
- Live service dashboards
-
Phase 05
Optimise
Every quarter- FinOps and performance tuning
- Recovery drill and review
Durations are typical; every engagement is scoped after the assessment.
Service levels
Service levels we sign up to
Our commitments are written into every contract and reported every month.
24/7/365
Operations centre coverage
99.99%
Availability SLA target on managed platforms
15 min
Priority-1 response time
Quarterly
Recovery drills with signed reports
| Severity | Example | Response | Updates |
|---|---|---|---|
| P1 · Critical | Production down or data at risk | 15 min | Every 30 min |
| P2 · High | Major degradation with no workaround | 30 min | Every 2 hours |
| P3 · Medium | Limited impact, workaround available | 4 hours | Daily |
| P4 · Low | Question or planned change | 1 business day | On resolution |
Figures are LoopStack’s standard service targets. Final service levels are agreed per workload and set out in each contract.
Security & compliance
Security built into every layer
Defence in depth, from governance down to your data, with evidence ready whenever auditors ask.
Zero-trust identity
Single sign-on, multi-factor authentication and least-privilege access for every operator.
Encryption everywhere
Data encrypted in transit and at rest, with keys under your control.
24/7 threat monitoring
Security events correlated with operations alerts and handled around the clock.
Audit-ready evidence
Change, access and recovery-test records retained for auditors and regulators.
Frameworks we design and operate to
PDPLNCA ECCISO/IEC 27001SOC 2PCI DSSNIST CSFCIS BenchmarksGDPRWe design and operate client environments in line with these frameworks. Certification of a client environment is scoped separately for each engagement.
Let’s keep you running
Book a 30-minute resilience review. We’ll map your critical workloads, your current recovery objectives and the fastest path to closing the gap.